SEC Commissioner Peirce Calls for Less KYC Data Collection
Hester Peirce urged greater use of attribute-based credentials and zero-knowledge proofs to reduce unnecessary personal-data collection while verifying eligibility.
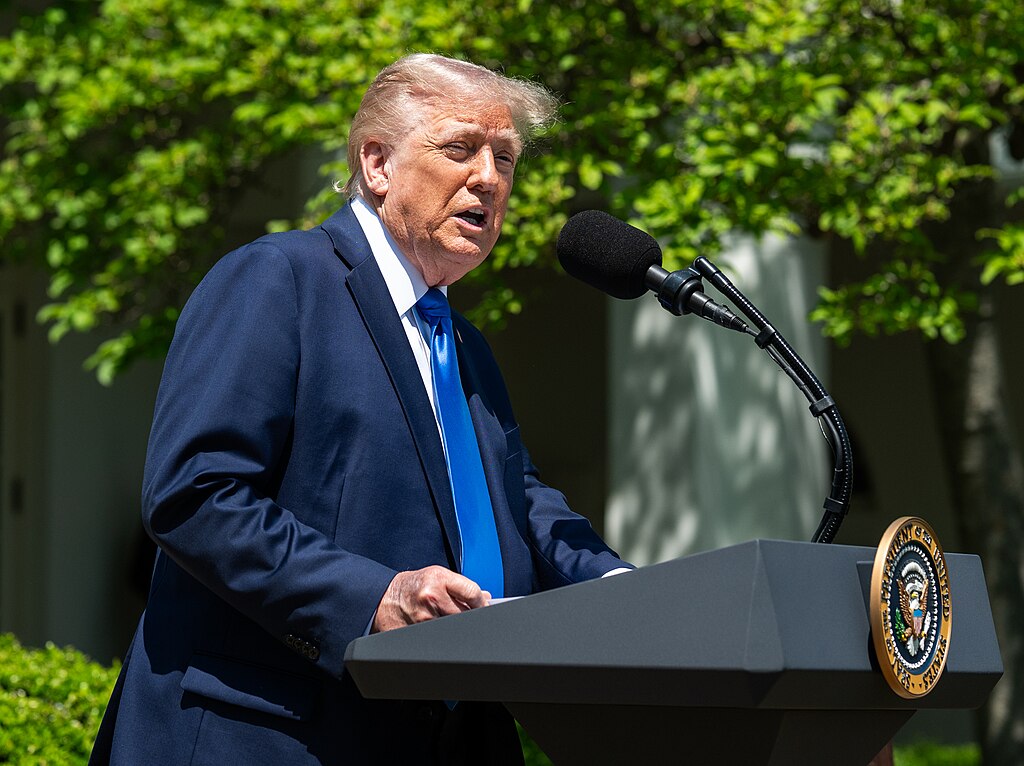
SEC Commissioner Hester Peirce urged financial regulators to reduce unnecessary personal-data collection by expanding the use of cryptographic verification during a Sept. 23 speech in New York.
Speaking at the 2026 SIFMA Digital Assets Conference, Peirce criticized know-your-customer and anti-money-laundering systems that may require institutions to gather names, birth dates, addresses, identification numbers and transaction details even when they need to confirm only a narrower qualification.
“Down one path lies the status quo: more data collection, more intermediary surveillance, more ‘know your customer’ requirements that turn our financial rails into a panopticon,” Peirce said.
Peirce called for greater use of attribute-based credentials and zero-knowledge proofs. These tools can verify facts such as age, citizenship, accredited-investor status or the absence of a sanctions-list match without disclosing the underlying personal information.
“A zero-knowledge proof can tell a counterparty ‘Yes, this person meets your requirement’ without that counterparty knowing your name, income, or address,” Peirce said.
She also urged regulators to let financial firms rely more on trusted third-party identity verification. That approach would reduce the need for each institution to independently copy and retain the same customer records.
Separate disclosures from Trezor detailed recent breaches involving third-party service providers. Trezor said a Sept. 9 breach at its email provider, Brevo, exposed 347,149 marketing contacts, while no wallet, product or account system was affected.
Trezor also said a separate breach at shipping provider ShipMonk affected 80,689 customers, including about 67,000 additional U.S. customers. The exposed information included names, email addresses, phone numbers, shipping addresses and order numbers.
Trezor said the Brevo incident enabled phishing emails through a trusted communication channel. It also said the ShipMonk exposure could increase phishing and physical-security risks.
Peirce described large stores of personal information as a security liability for governments and private companies.
“Every additional field of personal and confidential business data the government collects and retains incrementally increases the likelihood the government or a private party will mishandle it by accident or on purpose,” she said.
“The bigger haystack, however, makes it harder to find the needles.”
Peirce said the speech came during her “penultimate week” as an SEC commissioner. She said the views were her own and did not necessarily represent the agency or its other commissioners.