
 Add as a preferred source on Google
Midnight Mimosa Malware Found Preinstalled on Android Phones in More Than 150 Countries
The firmware-level malware affects some low-cost MediaTek devices and has been found in more than 150 countries, including the United States.

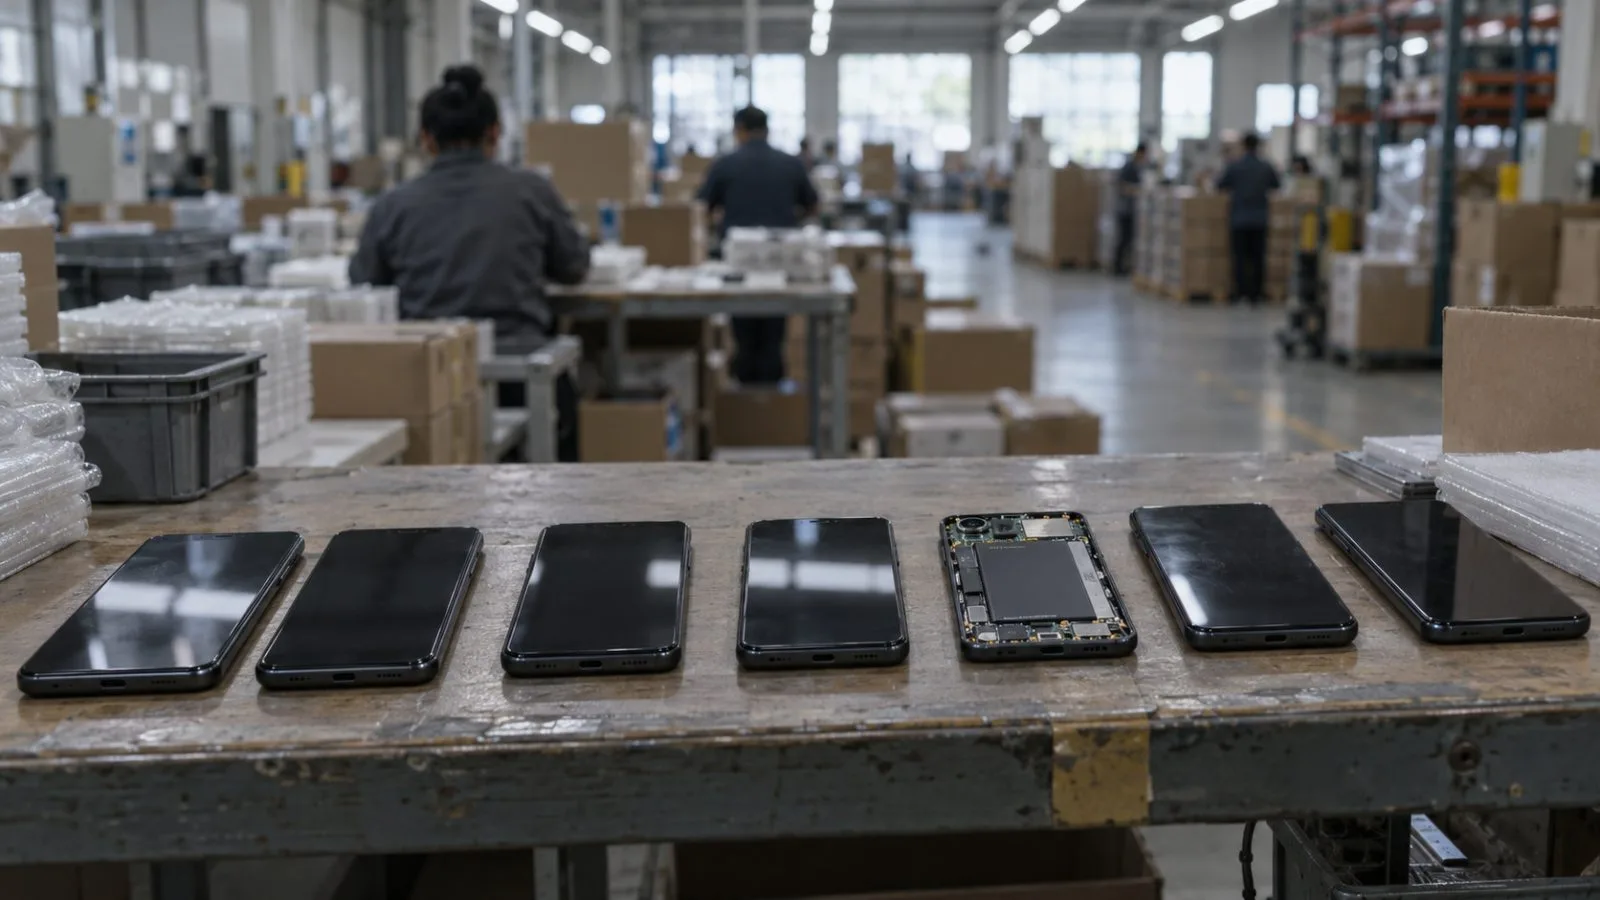
Thousands of budget Android phones shipped with Midnight Mimosa malware preinstalled in their firmware, exposing devices in more than 150 countries to software that operates with system-level privileges.
The malware affects some low-cost phones built with MediaTek chips. The highest-volume models identified were the Doogee S200 X and Cubot KINGKONG X, along with knockoff devices posing as Samsung and Apple phones.
Because the malicious software is embedded in the firmware, it is present before the owner switches on the device and cannot be removed through ordinary app-uninstallation methods. Its system-level access allows it to install and remove applications, grant permissions and load code sent from a remote server.
At least 32 disguised apps have been deployed through the malware, including fake weather, app-lock, file-manager, icon-tool, OCR and audio-editing tools. Thirteen apps on the Google Play Store also carried the same ad-fraud code.
The affected phones were concentrated most heavily in Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. The geographic spread indicates that the issue extends beyond a single market or device model.
Compromised devices can be converted into residential proxy nodes, which route internet traffic through the phone, or incorporated into botnets. Those botnets can support distributed denial-of-service attacks by directing large volumes of traffic at a target.
The point in the supply chain where Midnight Mimosa is added to the devices has not been identified. Bitdefender did not accuse Doogee, Cubot or the other named brands of installing the malware.
Simon Yoon
ReporterSimon Yoon reports on blockchain technology for TokenPost. Send corrections or tips to info@tokenpost.com.