
 Add as a preferred source on Google
Binance hack exposes need for stronger security and staff training
TRM Labs' Ari Redbord said the Binance hack highlights the need for staff training, shared security standards and cooperation to freeze stolen funds.
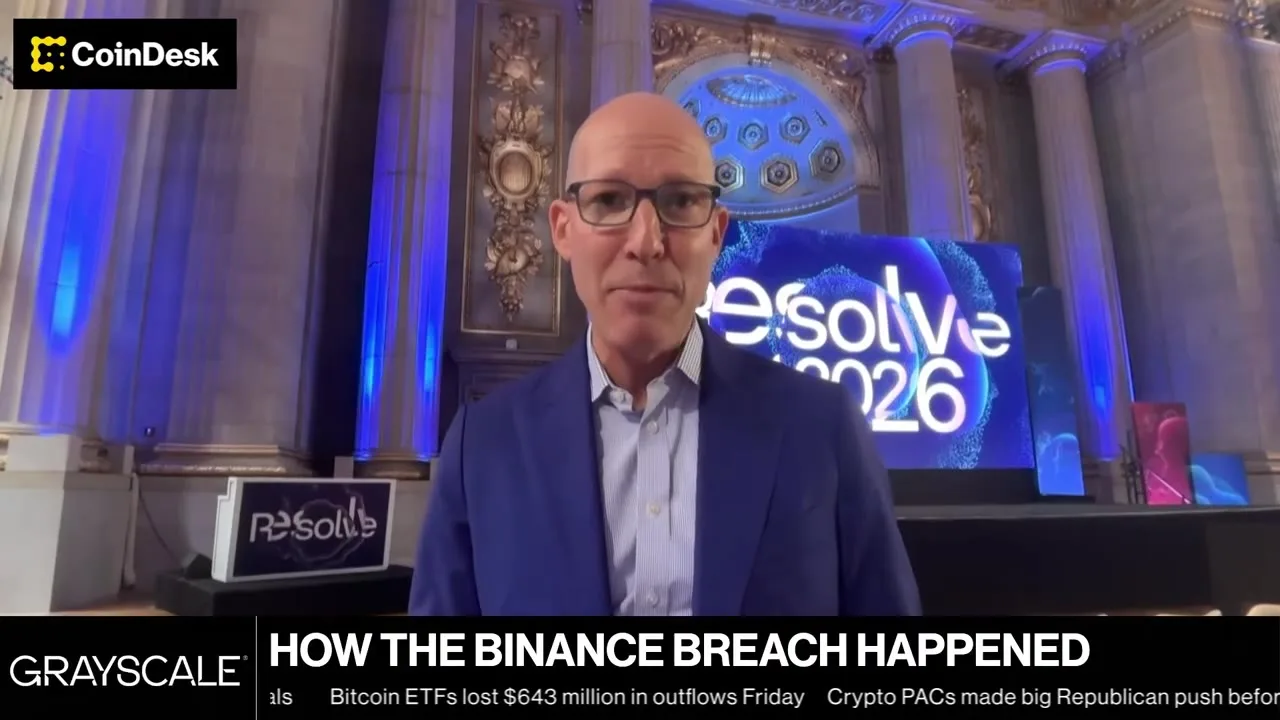
The Binance hack has underscored the need for stronger cybersecurity training, information sharing and cooperation to freeze stolen cryptocurrency across the industry.
Defending against sophisticated state-backed attackers requires exchanges to protect both their systems and the people who can grant access to them, according to TRM Labs global head of policy Ari Redbord.
In a November 2 interview on CoinDesk's Public Keys, Redbord attributed the Binance attack to North Korea and outlined the challenges facing the industry's response. He said an attack capable of breaching Binance could happen to any cryptocurrency business.
Redbord put the theft at about $6 billion, describing its scale as unprecedented and comparing it with North Korea's economy of more than $20 billion. He characterized it as the largest bank robbery in human history, extending beyond cryptocurrency's previous security failures.
Binance's financial capacity could make a substantial difference for affected users, he said. Another business might struggle to cover losses of that size. Even a sophisticated company with cybersecurity controls can be breached by a highly capable attacker, he added, calling for stronger defenses alongside action against those responsible.
Redbord pointed to stablecoin issuers as an important part of the recovery effort. He said Tether and Circle helped take back about 40% of the stolen assets in the attack's early stages through capabilities used to freeze tokens.
TRM Labs' Beacon Network, a public-private information-sharing network, also supported coordinated efforts to freeze funds, he said. TRM had worked closely with almost every cryptocurrency exchange in the network over roughly 36 hours, with participants responding to alerts in real time. Redbord said he had seen more alerts over the preceding 36 to 72 hours than ever before, alongside unprecedented cooperation among exchanges.
Redbord deferred to Binance on the precise way its security was breached, saying the account of the intrusion was still developing. He nevertheless highlighted North Korea's growing skill in social engineering, in which attackers manipulate people to gain access. Repeated compromises involving personnel make cybersecurity training critical, he said.
The response needs to extend beyond major exchanges to the wider cryptocurrency ecosystem, Redbord said. Protecting people is part of strengthening cybersecurity, and decentralized finance services and large exchanges alike need common security standards or, at a minimum, shared best practices.
Riza Dagoc
Riza Dagoc reports on regulation, investing and the digital-asset business for TokenPost. Send corrections or tips to info@tokenpost.com.